You built a cool demo. It worked once. Then it broke in production because the model decided to take a detour you didn't plan for. This is the classic trap of early-stage LLM engineering. You’re trying to decide between two paths: rigidly controlling every step with prompt chaining or letting an agent figure out its own route. One feels safe but limited; the other feels powerful but chaotic. The truth? Neither is universally "better." It depends entirely on whether your problem has a known path or requires discovery.
Most teams over-engineer their first solutions. They jump straight into complex agentic frameworks when a simple sequence of prompts would have done the job faster, cheaper, and more reliably. By September 2026, the industry has matured enough that we can look at hard data rather than hype. Let’s break down exactly when to use which pattern, how they differ under the hood, and why mixing them might be your best bet.
What Actually Is Prompt Chaining?
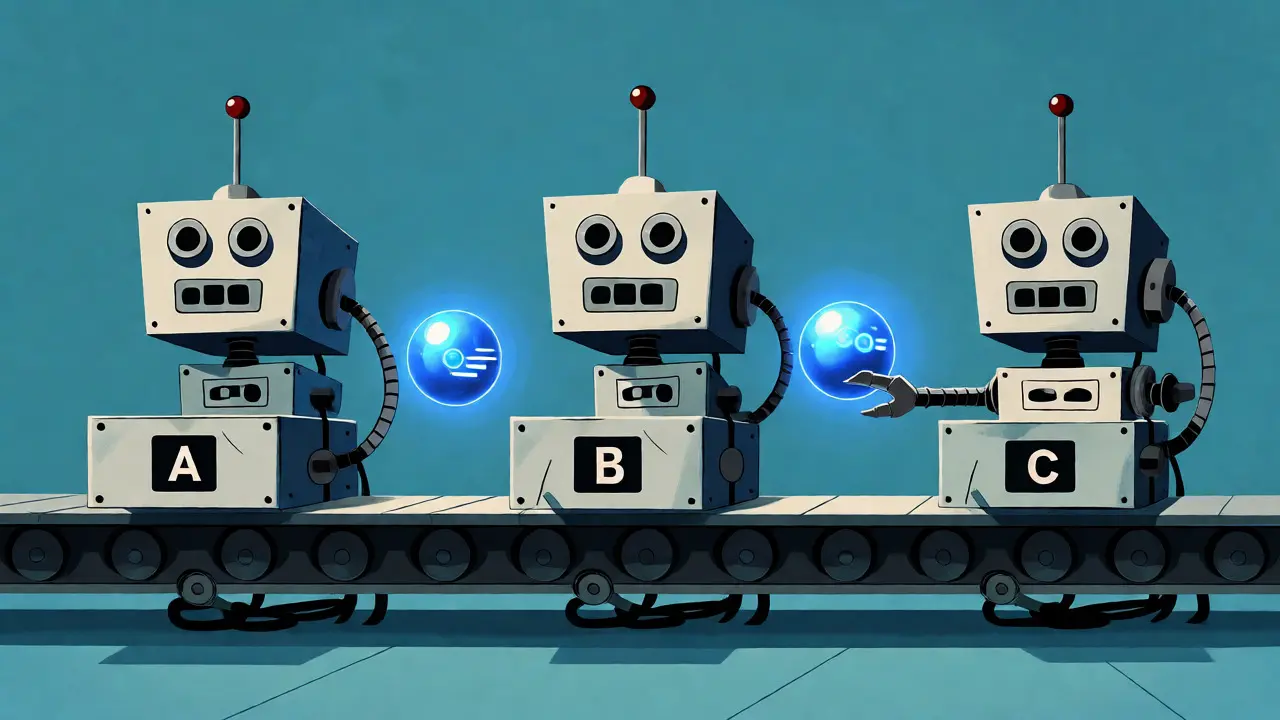
Prompt Chaining is a workflow pattern where the output of one Large Language Model (LLM) call sequentially feeds into the input of the next call. Think of it like an assembly line. Station A takes raw data and cleans it. Station B takes the clean data and summarizes it. Station C takes the summary and writes an email. Each station does one specific thing, passes the result forward, and then goes idle.
This approach is stateless by default. Step 3 doesn’t know what happened in Step 1 unless you explicitly pass that information along. Because the sequence is fixed-A → B → C-you have total control. If Step B fails, you know exactly why. You can insert "gates" or checkpoints between steps to validate outputs before proceeding. For example, after generating a draft, you can run a separate check to ensure it meets legal compliance before moving to the final formatting stage.
Why do engineers love this? Predictability. In regulated industries like finance or healthcare, you need an audit trail. When UnitedHealth Group implemented a HIPAA-compliant patient data pipeline, they used chained prompts because they could verify each step independently. If a mistake happens, you don’t have to debug a black box; you just look at the specific link in the chain that failed.
The Rise of Agentic Planning
On the flip side, Agentic Planning refers to goal-driven autonomous systems that maintain state through memory, execute multi-step processes with dynamic adaptation, and frequently utilize external tools. Unlike chaining, an agent doesn’t follow a pre-written script. It starts with a goal (e.g., "Research competitor pricing") and figures out the steps itself.
An agent might realize it needs to search the web, then parse a PDF, then write code to analyze the data, then summarize the findings. Crucially, if the web search returns irrelevant results, the agent can decide to change its search query and try again. This loop-plan, act, observe, reflect-is what makes agents powerful for open-ended problems. GitHub’s Copilot Workspace uses this logic. It doesn’t know beforehand how many files need changing for a specific feature request; it discovers that during execution.
But this flexibility comes at a cost. Agents are stateful. They remember previous actions, which consumes context window space. They also require sophisticated error handling. If an agent gets stuck in a loop, retrying the same bad action forever, you need mechanisms to detect and break that cycle. This complexity explains why agentic implementations often take 8-12 weeks to stabilize compared to the 2-3 weeks typical for robust chains.
Performance Metrics: Cost, Speed, and Accuracy
Let’s look at the numbers. Benchmarking from AI Competence in late 2024 showed that prompt chaining typically consumes 30-40% fewer tokens per execution than agentic workflows. Why? Because agents spend tokens thinking about what to do next, reflecting on past errors, and re-planning. Chains just execute.
For high-volume tasks, this difference matters. Processing 10,000 documents with a chain might cost $12, while an equivalent agentic workflow could cost $39. That’s a 68% efficiency gap. However, accuracy tells a different story. In fixed, linear processes, chains boast 27% higher accuracy because there’s no room for creative deviation. But in dynamic scenarios where inputs vary wildly, agents achieve 42% better results because they can adapt to unforeseen edge cases.
| Metric | Prompt Chaining | Agentic Planning |
|---|---|---|
| Token Consumption | Low (30-40% less) | High (2.5-3.5x more resources) |
| Implementation Time | 2-3 Weeks | 8-12 Weeks |
| Auditability | High (Traceable steps) | Low (Black-box execution) |
| Best Use Case | Linear, predictable workflows | Complex, adaptive problem solving |
| Error Rate | Lower in defined tasks | Higher due to unpredictability |
One developer on Reddit reported reducing errors from 12% to 3.2% simply by switching from an agent to a chain for document processing. Another data scientist noted that for analyzing unstructured scientific papers, the agent saved 14 hours per analysis because it could dynamically adjust its search strategy. Context is everything.
When to Choose Which Pattern
How do you decide? Ask yourself these three questions:
- Is the path known? If you can write down the exact steps required to solve the task, use prompt chaining. If the steps depend on intermediate results, consider an agent.
- Is cost a primary constraint? If you’re processing thousands of items daily, the token savings of chaining are massive. If you’re doing low-volume, high-value research, the extra cost of an agent is negligible compared to the value of better insights.
- Do you need strict compliance? Financial services firms often mandate chaining because regulators need to see exactly how a decision was made. Agents are harder to audit because their internal reasoning paths can vary run-to-run.
Stanford HAI researchers found that 68% of successful Fortune 500 deployments started with prompt chaining. They only added agentic elements later, specifically for parts of the workflow that resisted rigid definition. Don’t start with the most complex solution. Start with the simplest one that works.
The Hybrid Approach: Best of Both Worlds
Here’s the secret nobody talks about: you rarely choose just one. Most modern architectures are hybrid. You use prompt chaining for the reliable backbone of your application-data ingestion, cleaning, standard formatting-and drop in an agent for the tricky middle part where judgment is required.
For instance, imagine a customer support bot. You use a chain to classify the ticket type and pull up the user’s history. Then, you hand off to an agent to draft a personalized response that requires synthesizing policy documents and tone guidelines. Finally, you return to a chain to format the email and log the interaction. This gives you the reliability of chains at the edges and the intelligence of agents in the core.
Frameworks like LangGraph and CrewAI make this easier by allowing "chain-to-agent handoffs." If a chain’s confidence score drops below a threshold, it automatically escalates to an agent. This prevents over-engineering while ensuring quality. Anthropic’s recent updates even introduced "adaptive chaining," which adds limited reflection capabilities to standard chains, bridging the gap further.
Common Pitfalls to Avoid
Even experienced teams fall into traps. The biggest one is using an agent for a task that could be solved with a single prompt. If you can solve it with one shot, don’t build a chain. If you can solve it with a chain, don’t build an agent. MIT’s AI Policy Forum documented cases where unnecessary agentic complexity increased implementation costs by 3.7x and delayed time-to-value by five months.
Another pitfall is poor state management in agents. Developers often forget to prune the conversation history, leading to bloated contexts and slower responses. Always implement memory limits. Similarly, in chaining, avoid passing too much context between steps. Keep each step focused. If Step B needs info from Step A, pass only the relevant fields, not the entire JSON blob.
Finally, ignore observability at your peril. With agents, you must instrument every tool call and decision point. Without logs, debugging an agent that went off-rails is like finding a needle in a haystack. With chains, add validation gates. If an output doesn’t match expected schema, fail fast rather than propagating garbage downstream.
Frequently Asked Questions
Is prompt chaining obsolete now that agents are popular?
No, prompt chaining is far from obsolete. In fact, Gartner reports that 68% of enterprise LLM implementations still rely on chaining for core business processes. Its predictability, lower cost, and ease of debugging make it the preferred choice for stable, repeatable tasks. Agents are complementary, not replacements.
Which is cheaper to run in production?
Prompt chaining is significantly cheaper, typically consuming 30-40% fewer tokens per execution. Agentic workflows require 2.5-3.5x more computational resources due to reflective loops and retries. For high-volume applications, this cost difference can determine project viability.
Can I combine prompt chaining and agentic planning?
Yes, and you should. Hybrid architectures are becoming the industry standard. Use chaining for deterministic steps like data parsing and formatting, and employ agents for complex reasoning or dynamic decision-making within the workflow. Frameworks like LangGraph facilitate seamless handoffs between these modes.
How long does it take to implement each pattern?
Experienced developers can implement robust prompt chaining workflows in 2-3 weeks. Agentic systems typically require 8-12 weeks due to the complexity of state management, error handling, and tuning the agent's behavior. The learning curve for effective agentic implementation is also steeper, requiring specialized knowledge in orchestration patterns.
What are the main risks of using agentic planning?
The primary risks include unpredictable token consumption, difficulty in debugging non-deterministic paths, and higher implementation failure rates if simpler alternatives weren't considered. Enterprises adopting agents without assessing chaining alternatives experience 3.2x higher failure rates according to Conviction Partners.